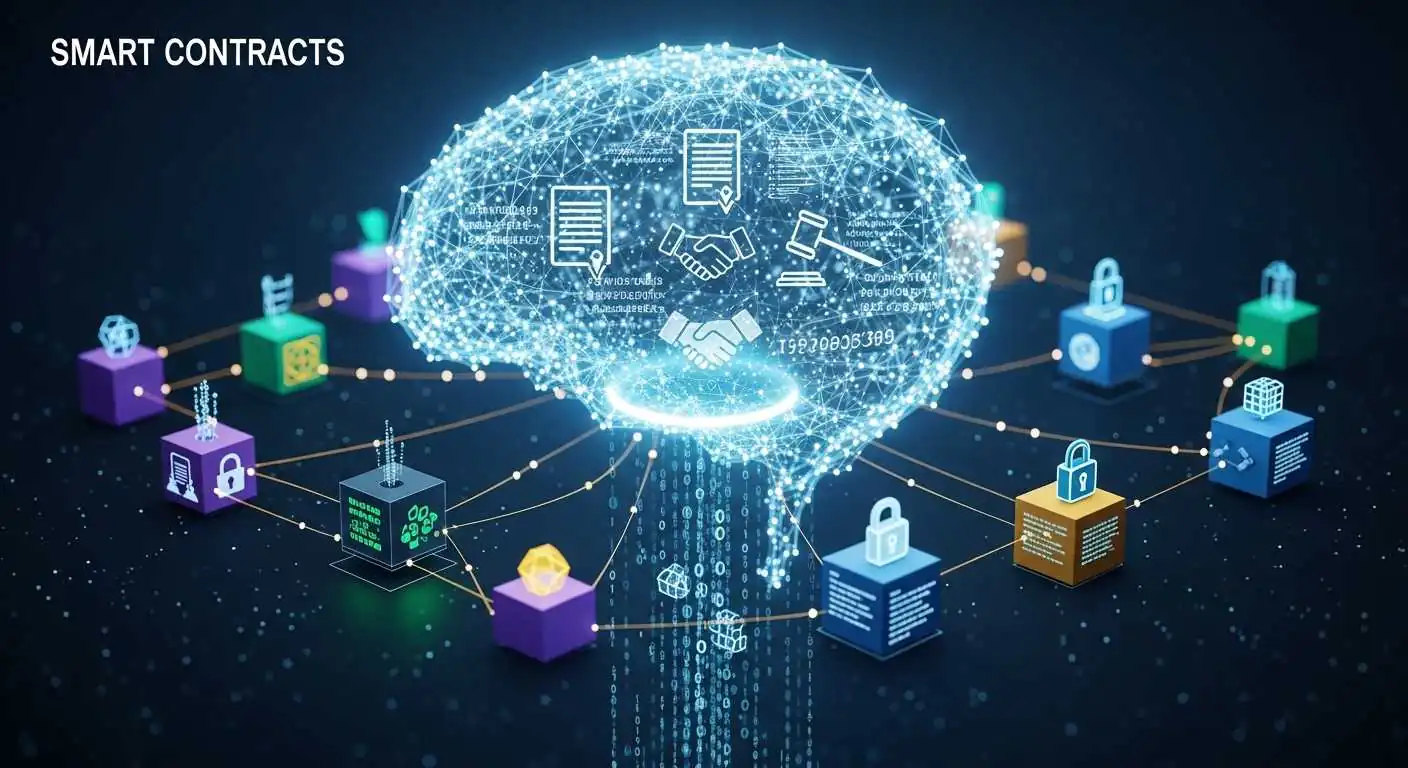
Smart contracts are one of the most important innovations to emerge from blockchain technology. At a basic level, a smart contract is a program stored on a blockchain that runs when predefined conditions are met. Ethereum’s developer documentation describes smart contracts as programs at specific blockchain addresses that contain data and functions and can execute when triggered by a transaction. That simple description matters because it captures why smart contracts changed the blockchain conversation: they turned blockchains from passive ledgers into programmable systems for money, logic, and coordination.
Their appeal comes from automation and trust minimization. Instead of relying on a central operator to check conditions, approve actions, and update records, the logic is embedded into code and enforced by a distributed network. This has made smart contracts foundational for decentralized finance, NFT ecosystems, token issuance, on-chain governance, and a growing range of enterprise experiments. At the same time, smart contracts are not inherently “safe” or “smart” in the everyday sense. They only do what the code tells them to do, and mistakes can be permanent and expensive. Ethereum’s security guidance emphasizes access controls, testing, independent review, and secure governance as core requirements for safe smart contract design.
What Smart Contracts Actually Do
A useful way to understand smart contracts is to think of them as rule engines for digital agreements and asset flows. A traditional contract states what parties agree to do. A smart contract goes further by automating part of that process. If a condition is met, the contract executes the next step automatically. This might mean transferring tokens, issuing rewards, releasing collateral, minting a digital asset, or recording a governance vote.
That is why smart contracts are so powerful in blockchain systems. They reduce dependence on manual enforcement and create predictable execution. Ethereum’s documentation notes that smart contracts can use offchain data through oracles, which expands their usefulness beyond purely on-chain events. But the same documentation also points out limitations, including contract size constraints and the need to carefully design around blockchain execution costs. In other words, smart contracts are powerful, but they are still bounded by technical realities.
The Main Benefits of Smart Contracts
The first major benefit is automation. Once deployed, a contract can execute rules continuously without waiting for office hours, manual approval chains, or centralized administrators. This is a big reason they became so important in decentralized finance, where markets and protocols run at all hours.
The second benefit is transparency. On public blockchains, contract code and transaction history can often be inspected by anyone. That does not guarantee understanding, but it does create a much more auditable system than closed financial infrastructure. Users, researchers, and auditors can evaluate how a contract is supposed to behave and compare that to what it actually does on-chain. Ethereum’s developer resources emphasize this transparency as part of the Ethereum stack’s broader value for builders.
The third benefit is composability. Smart contracts can interact with other smart contracts, which makes them building blocks rather than isolated applications. A lending protocol can plug into an oracle, a stablecoin, a decentralized exchange, and a governance module. This composability helped DeFi expand rapidly because new products could be assembled from existing on-chain components rather than built entirely from scratch.
There is also an efficiency argument. In settings where rules are clear and digitally verifiable, smart contracts can reduce friction, settlement delays, and some intermediary costs. That does not mean they eliminate every middle layer, but they often restructure where trust and control sit.
For businesses exploring blockchain products, this is where a smart contract development solution becomes strategically valuable. The goal is not simply to put legal or operational logic into code. It is to identify where automated execution and shared data visibility genuinely improve coordination.
Why Smart Contracts Matter More Now
Smart contracts matter more now because they sit inside a much larger digital asset economy than they did a few years ago. CoinGecko’s 2025 Q3 Crypto Industry Report noted that total crypto market capitalization rose to $4.0 trillion in Q3 2025, while DeFi market capitalization climbed 40.2% in the same quarter and decentralized perpetual exchange volume hit a record $1.8 trillion for the quarter. Those figures show that smart-contract-driven systems are not niche prototypes anymore. They are supporting meaningful market infrastructure.
Stablecoins are also part of this story. CoinGecko reported that stablecoin market capitalization reached a record $287.6 billion in Q3 2025, and later educational coverage from CoinGecko noted that the stablecoin market crossed $300 billion in 2025. Since stablecoins rely heavily on smart contracts for issuance, transfers, treasury operations, and DeFi integrations, their growth is another sign that programmable financial infrastructure is becoming more central, not less.
Real-World Applications of Smart Contracts
The most visible application is decentralized finance. Lending, borrowing, trading, staking, and derivatives markets all rely on smart contracts to manage collateral, calculate rates, process swaps, and distribute rewards. Instead of a bank or broker handling these actions behind the scenes, the blockchain executes them through code.
NFT ecosystems are another major use case. Smart contracts define token ownership, transfer logic, minting rules, royalty mechanisms, and marketplace interactions. This is what allows creators and collectors to interact with digital assets in ways that are programmable and verifiable on-chain.
Smart contracts also support governance. DAOs and other blockchain-based governance systems use them to manage voting rights, proposal execution, treasury movements, and timelocks. Ethereum’s security guidance specifically calls out secure governance system design as an essential part of smart contract safety, which reflects how important governance logic has become in modern protocols.
Enterprise and infrastructure use cases are still developing, but the practical logic is clear. Supply chains can use smart contracts to automate milestone tracking or conditional payments. Insurance systems can use them for parametric triggers if trusted external data is available. Tokenized assets can use them to manage transfer rules, settlement, and ownership records. The value is strongest where rules are clear, events can be verified, and multiple parties need a shared execution layer.
This is why many businesses now evaluate not just blockchain integration, but whether they need a smart contract development agency or a more specialized implementation partner. The challenge is often less about writing code and more about designing robust logic, permissions, and upgrade strategies around real commercial workflows.
The Biggest Risks in Smart Contracts
The core risk is simple: smart contracts are unforgiving. If the code contains a bug, weak access control, flawed business logic, or unsafe integration, the blockchain may execute that mistake exactly as written. Solidity’s security considerations stress that smart contract security is never fully exhaustive and that developers must think beyond obvious bugs to broader system behavior.
This is not a theoretical issue. Chainalysis reported that more than $2.17 billion had been stolen from cryptocurrency services by mid-2025, already exceeding the full year of 2024, and later reported that total crypto theft reached $3.4 billion in 2025, with North Korean actors alone responsible for $2.02 billion. Not every one of these incidents was caused by a smart contract flaw, but the data makes one thing clear: systems that hold digital assets are attacked constantly, and weaknesses in code, governance, or operational controls can be devastating.
Another important recent example is Chainalysis’s report on the April 1, 2026 Drift Protocol hack, where Solana’s Drift Protocol lost $285 million in an attack linked preliminarily to privileged-access abuse. That case highlights a point people often miss: smart contract risk is not just about reentrancy or arithmetic errors. It is also about governance, permissions, key management, and the operational assumptions around privileged actions.
Common Vulnerability Categories
Access control failures are among the most serious problems. If an admin function is too broad, poorly protected, or misunderstood by users, funds and system integrity may be at risk. Ethereum’s security guidance explicitly puts proper access controls at the top of its recommendations.
Business logic flaws are another major category. A contract may compile correctly and still be exploitable because the intended rules can be manipulated through edge cases or unusual interactions. This is especially important in DeFi, where liquidation logic, pricing assumptions, and pool incentives can create vulnerabilities that are not obvious from syntax alone.
Oracle dependence also adds risk. Smart contracts often need external data, but if that data feed is weak, delayed, or manipulated, the contract may still execute “correctly” on bad inputs. Ethereum’s documentation points out that oracles are the solution for offchain data, but that also means they become a critical dependency.
Upgradeability is another tradeoff. Many teams want contracts that can evolve, but upgrade patterns add complexity and trust assumptions. A poorly designed upgrade system can undermine the very immutability that users expect from blockchain applications.
Why Audits and Secure Development Matter
Because of these risks, auditing has become a core part of smart contract delivery. OpenZeppelin’s readiness guide frames secure smart contract development as a lifecycle with six phases: Plan, Code, Test, Audit, Deploy, and Monitor. That structure matters because it treats security as an ongoing process rather than a last-minute scan.
OpenZeppelin’s security audit materials also note that their reviews involve examining system architecture and codebase collaboratively, with each line of code inspected by at least two security researchers and, when needed, techniques like fuzzing and invariant testing. That reflects the level of rigor serious smart contract systems require.
The practical lesson is that a smart contract development firm should not be judged only by how fast it can deploy. The more important questions are whether it tests thoroughly, designs for least privilege, documents assumptions, prepares for audits, and monitors systems after launch.
Smart Contracts Are Powerful, Not Magical
One reason smart contracts are sometimes misunderstood is that they are often presented as a replacement for trust altogether. That is too simplistic. Smart contracts shift trust. Users may trust code more than a central operator in some contexts, but they still need to trust the design choices, audits, governance mechanisms, oracle sources, and surrounding operational controls.
Ethereum’s security and scam-prevention materials also remind users to think about wallet security, transaction review, and spend limits. That reinforces a broader point: the safety of a smart contract ecosystem depends on both protocol-level engineering and user-level behavior. A good contract can still be undermined by phishing, bad approvals, or compromised keys.
Conclusion
Smart contracts are one of blockchain’s most meaningful contributions because they turn agreements, financial logic, and digital coordination into executable code. Their benefits are substantial: automation, transparency, composability, and the ability to build systems that do not rely as heavily on centralized intermediaries. Their applications already span DeFi, NFTs, governance, stablecoins, and growing enterprise experiments.
But their risks are just as real. Weak permissions, faulty logic, insecure integrations, and poor operational controls can turn smart contracts into expensive liabilities. The recent scale of crypto theft underscores how exposed these systems can be when security fails.